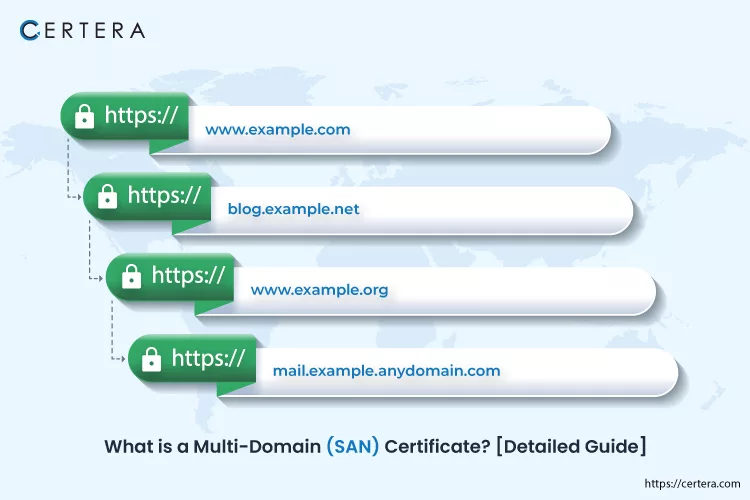
SAN SSL certificates are the ideal solution for small, medium-sized, and multinational companies wanting to secure several websites with a single SSL certificate. A SAN certificate offers unlimited FREE reissues and protects over 200 FQDN domains or websites across several web servers. Depending on the type and amount of validation,…
Before 2018, the transmission between the server and the client (browser) was in plain text format, which an eavesdropping third party could easily read. It was a severe problem in the context of – online banking, personal data privacy, etc. Hence, to overcome this, Google made it mandatory for all…
What is the SSL Handshake? SSL handshake establishes secure connections and safeguards sensitive data. This intricate process often operates silently in the background, ensuring that websites and applications uphold the highest encryption and authentication standards. In exploring the SSL/TLS handshake, we embark on its inner workings, understand its significance in…
In this blog, we have covered Sectigo RSA Domain Validation Certificate, answering all your questions and shedding light on its significance for enhancing website security. By the end of this article, you’ll clearly understand what this certificate is, how it works, and why it plays a crucial role in safeguarding…
In recent times, SSL/TLS certificate management is rapidly changing, with Google’s recent announcement to reduce certificate validity terms to just 90 days. This shift has profound implications for organizations and the industry, necessitating a shift from manual to automated SSL certificate lifecycle management (CLM). This article will explore the crucial…
Shortening of SSL/TLS certificate lifespans has been a persistent trend over the past decade. Google has announced its plans to reduce SSL/TLS certificate validity terms to 90 days. As an organization grappling with this significant shift, you may ponder the potential impact on your business. Or you can consider the…
Imagine the dismay of potential visitors when they encounter a daunting message in their browser warning them about the lack of security on your site. Fear not; we are here to illuminate a simple yet powerful solution: a secure sockets layer (SSL) certificate. At Certera, we understand the significance of…
OCSP stapling renders it more accessible and more rapid for a customer than ever to check the status of an SSL/TLS certificate’s revocation. It is an enhancement over the existing industry standard, OCSP. But what exactly is OCSP stapling, and why does it matter for the security of your website?…
You may undoubtedly come across the terms “root certificates” and “intermediate certificates” whenever you get an SSL certificate for your website. After all, it is normal to fail to differentiate the two terms. So, let’s get started without further delay. Since the ZIP archive package that you get in an…
The foundation of Public Key Infrastructure (PKI), which secures billions of online transactions, is the X.509 digital certificate standard. But what will happen if these certificates or the keys that go with them have an issue? They need to be revoked since it is clear that they can no longer be…
Browsers verify the validity of a website’s TLS certificate before connecting to it, and they display a warning message if the certificate has been revoked. OCSP, CRLs, OCSP must-staple, and OCSP stapling are revocations status-checking techniques browsers use. This article analyses and compares two techniques, named CRL vs OCSP. The…
Welcome! This article will discover a robust protocol and explore how it functions. ACME protocol, short for Automated Certificate Management Environment, is a seamless communication channel between Certificate Authorities (CAs) and various endpoints in a company’s digital ecosystem. ACME automates the management of Public Key Infrastructure (PKI) certificates used in…
If you have a website, you must have an SSL certificate. In general, you’re certainly aware of how SSL certificates work. It utilizes the Transport Layer Security (TLS) protocol to ensure that the communication between your website and the web browser (used by the user) is protected and secured. Furthermore,…
When you visit a website that opens with HTTPS, it is a validation that you use a certificate authority. But what are HTTPS and CA, and how do those approaches make your financial transactions and internet communications more secure? Certificate Authorities (CA) are an important component of the Internet. You might be unable to use…
SSL Offloading: A Breakthrough in Secure Data Transmission In today’s world of technology, ensuring that your website is secured against cyber-attacks is essential. SSL (Secure Socket Layer) encryption is one of the most effective techniques for doing this. SSL protects sensitive data by encrypting the traffic between the user’s browser…